Creuto: AI Technology & Product Insights
Stay informed with practical insights from the Creuto team on artificial intelligence, custom software, mobile applications, SaaS development, product engineering, technology trends, and digital transformation.
Latest posts
More posts
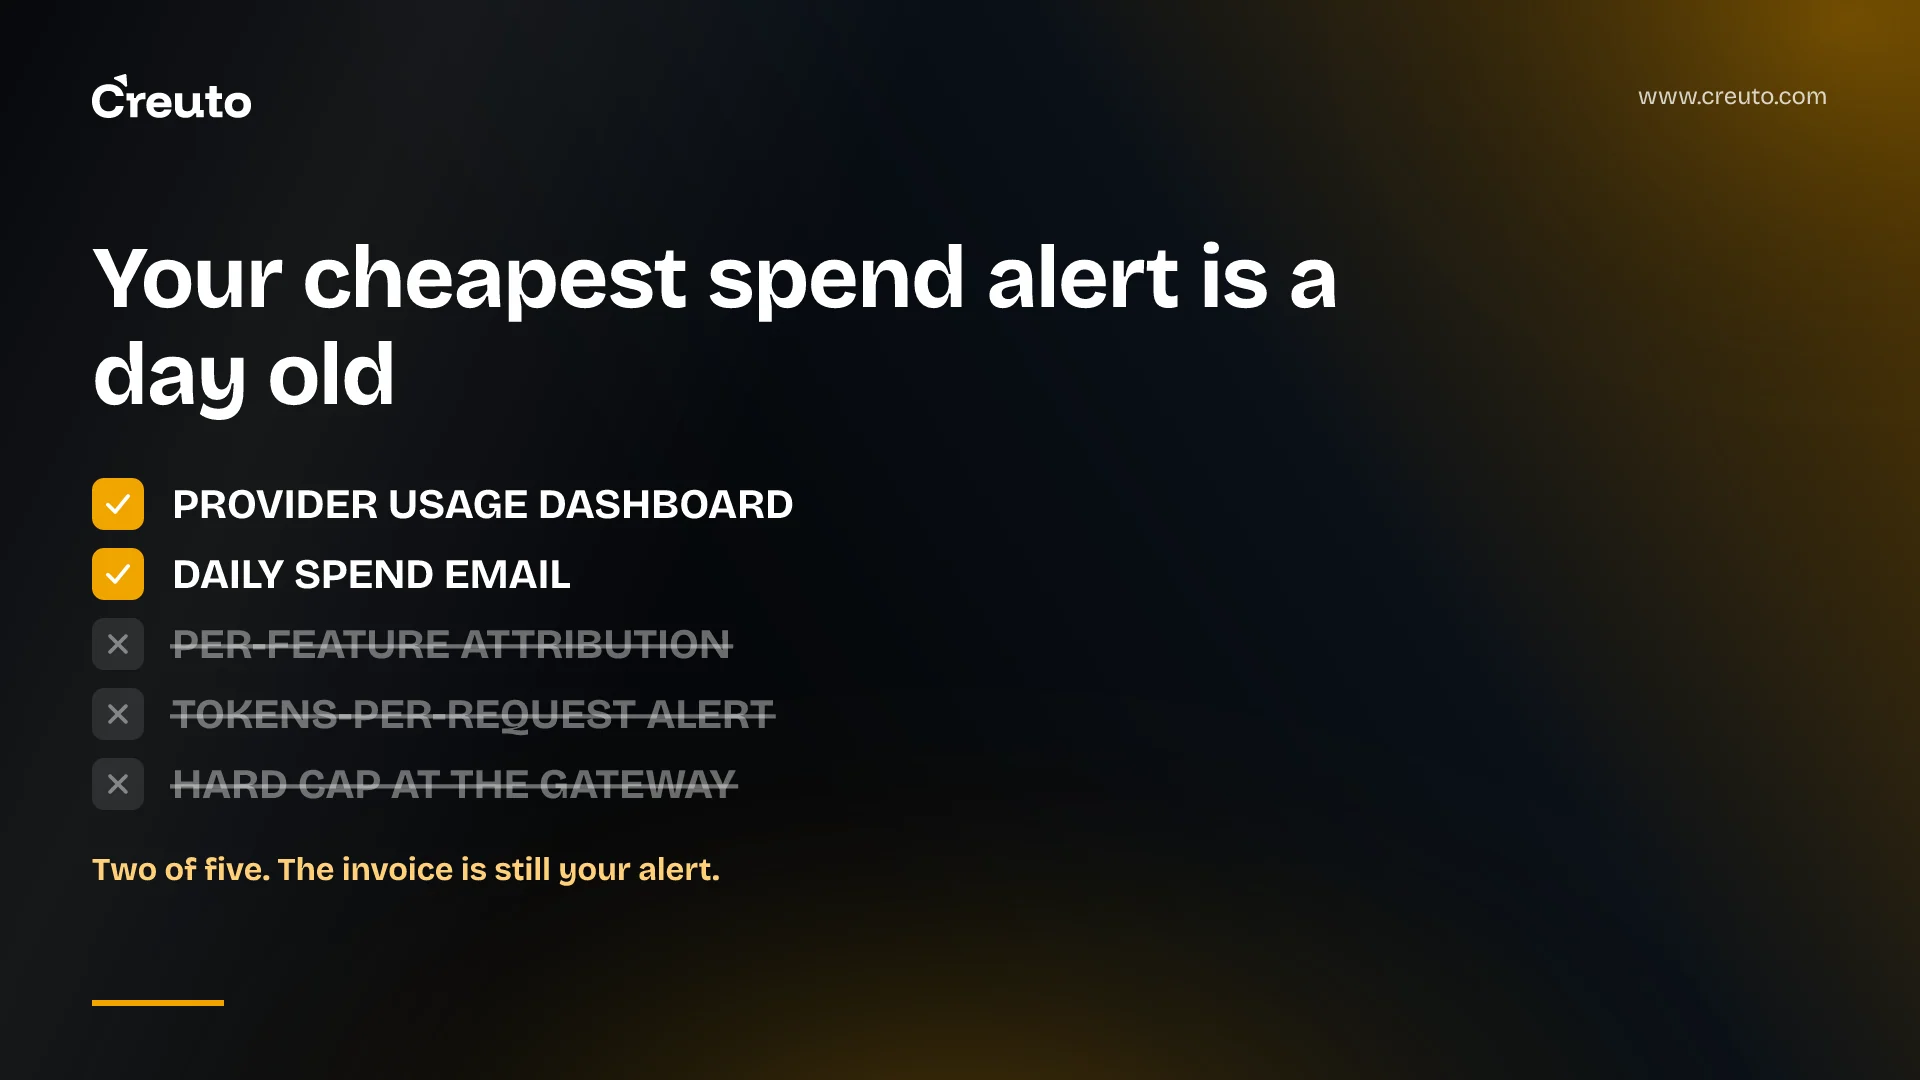
AI spend monitoring: catch model overuse before the bill
Every provider cost API buckets by day, so your spend alert is already stale. What OpenAI, Anthropic, Google and AI gateways can actually enforce, and why we alert on tokens per request instead.
Akash Mohapatra
Oct 1, 2026
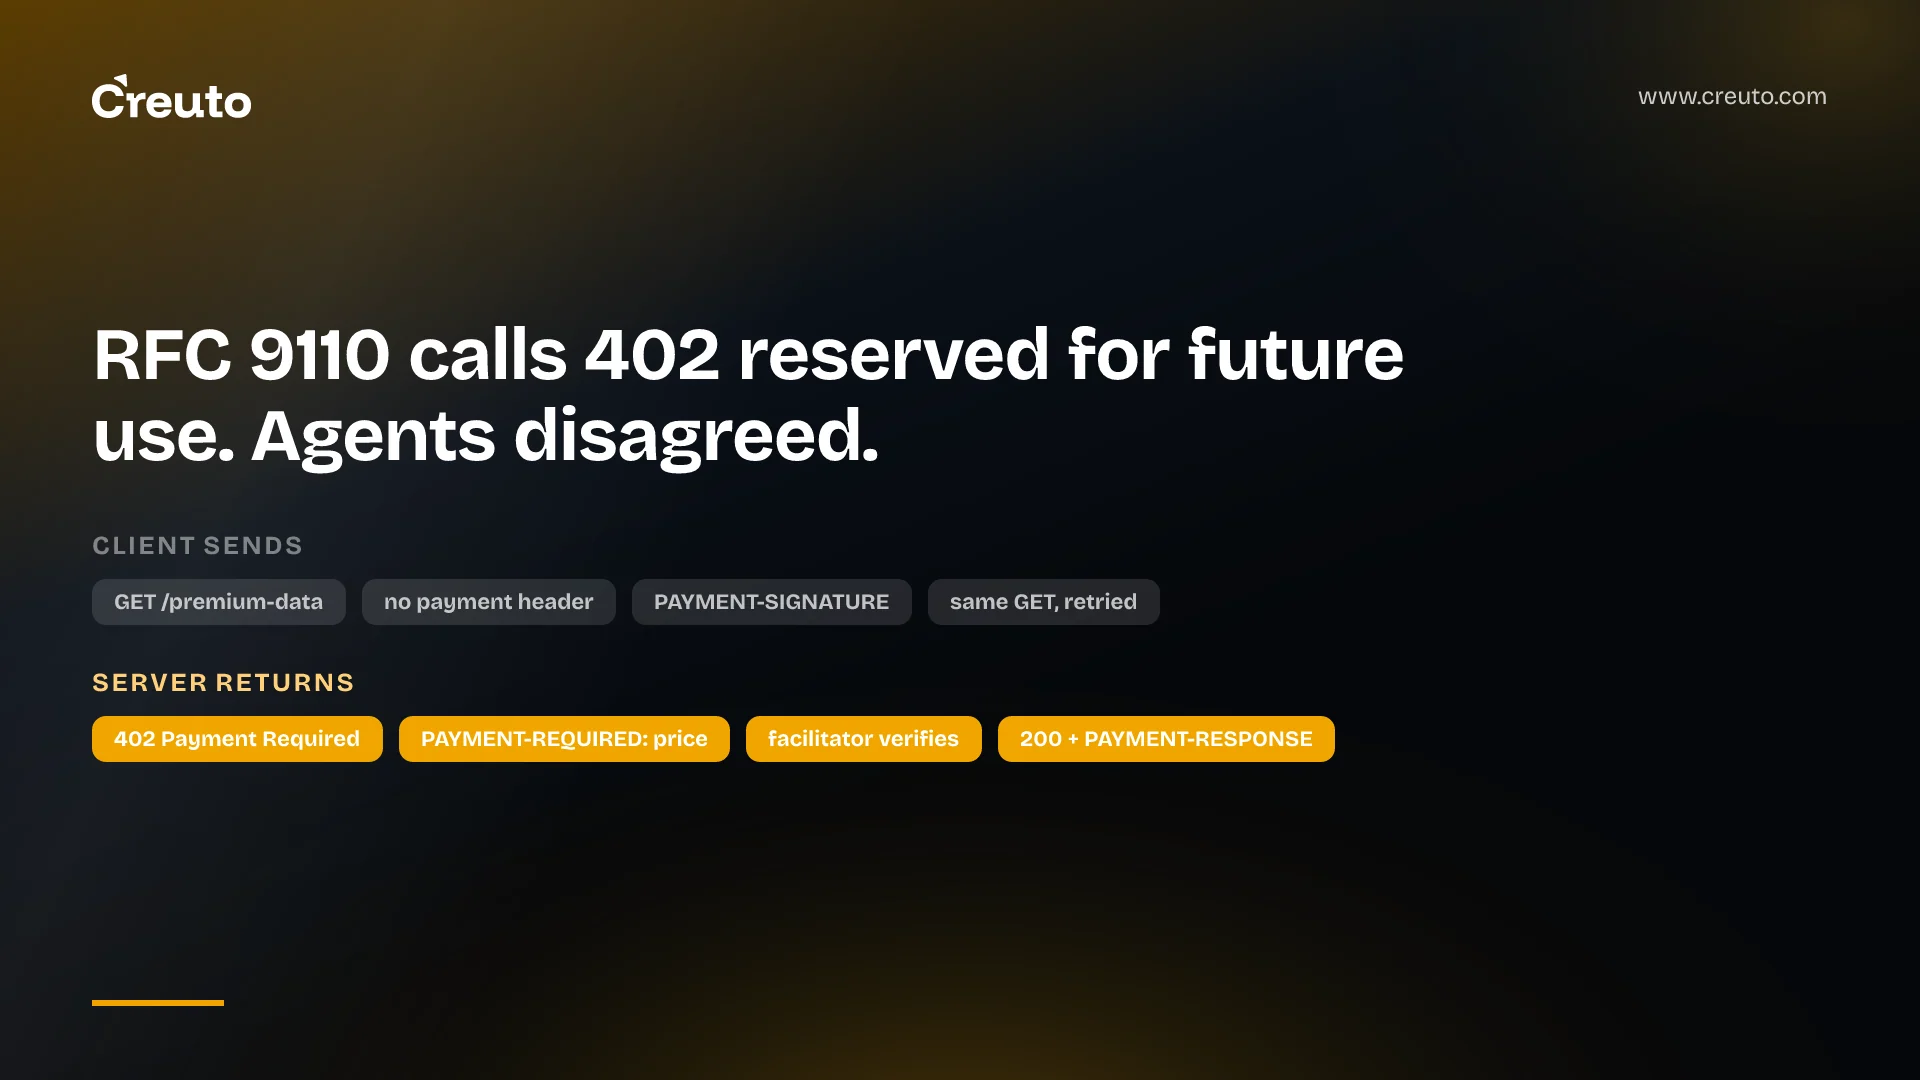
HTTP 402 Payment Required: charging agents per request
RFC 9110 calls 402 reserved for future use. Two Cloudflare products and the x402 specification now disagree. What the real header exchange looks like, and what you would have to build.
Akash Mohapatra
Sep 30, 2026
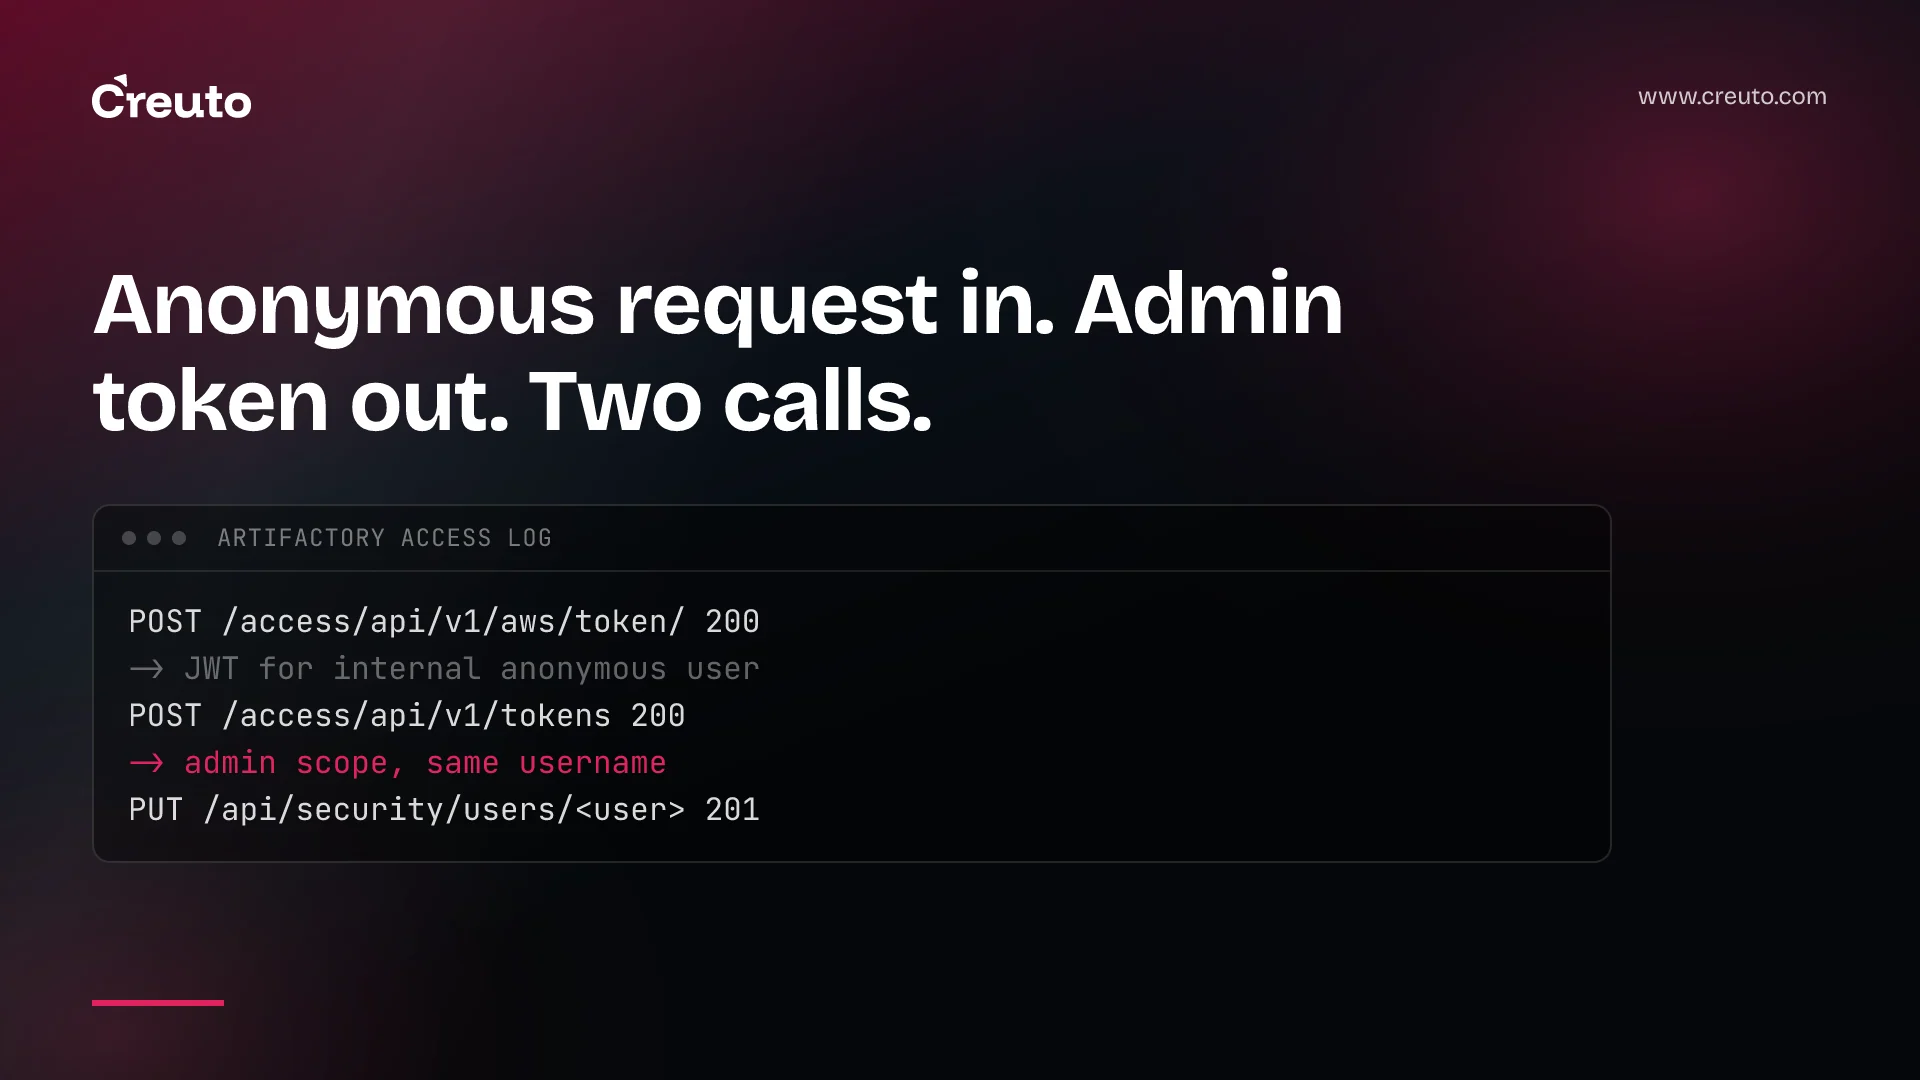
Artifactory vulnerability chain: patch now, assume breach
Three JFrog Artifactory CVEs are being exploited in the wild and all three are on CISA's KEV catalogue. Here is the per-branch patch matrix, the two-request escalation chain, and what to check once you have patched.
Akash Mohapatra
Sep 29, 2026
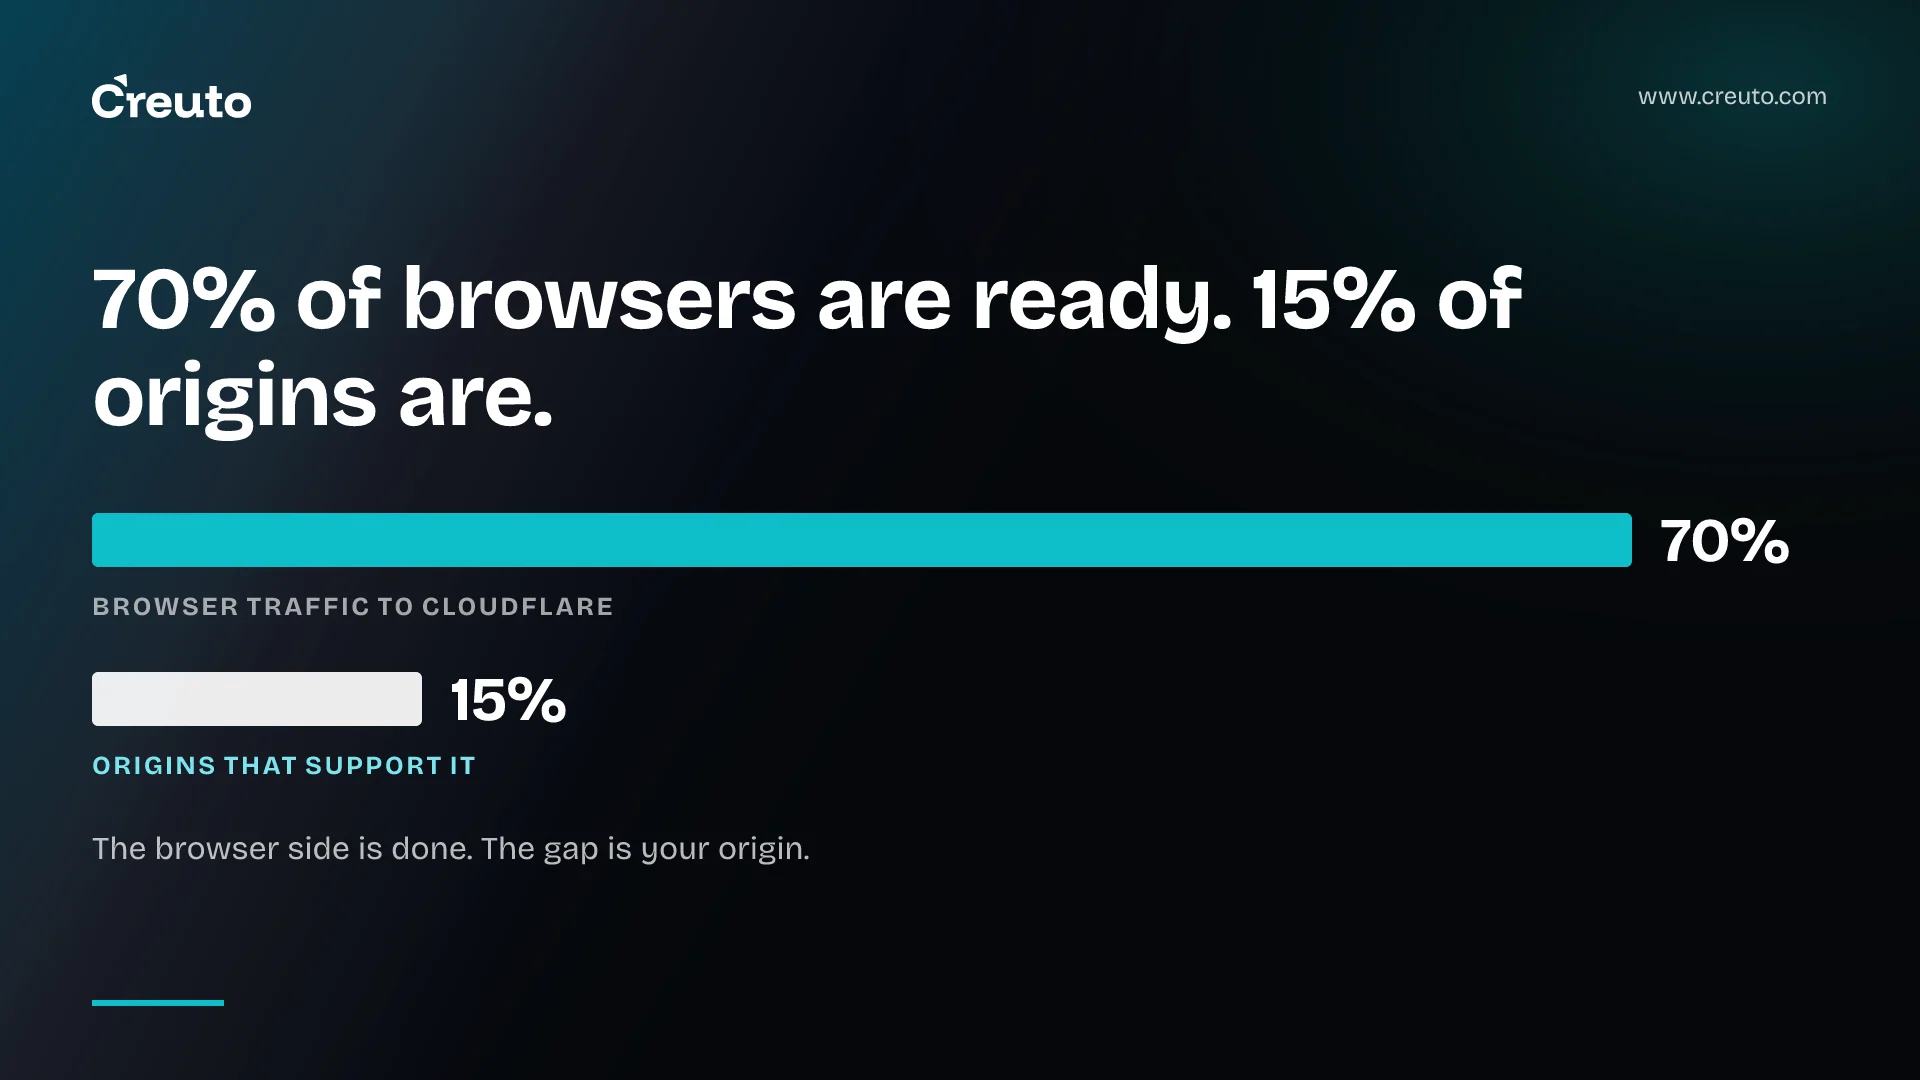
Post-quantum encryption check: what your domain uses
Cloudflare now surfaces the negotiated TLS key exchange group per request in Traffic Analytics, Log Explorer and Logpush. About 70% of browser traffic uses hybrid ML-KEM; about 15% of origins do. Here is how to read the gap.
Akash Mohapatra
Sep 29, 2026
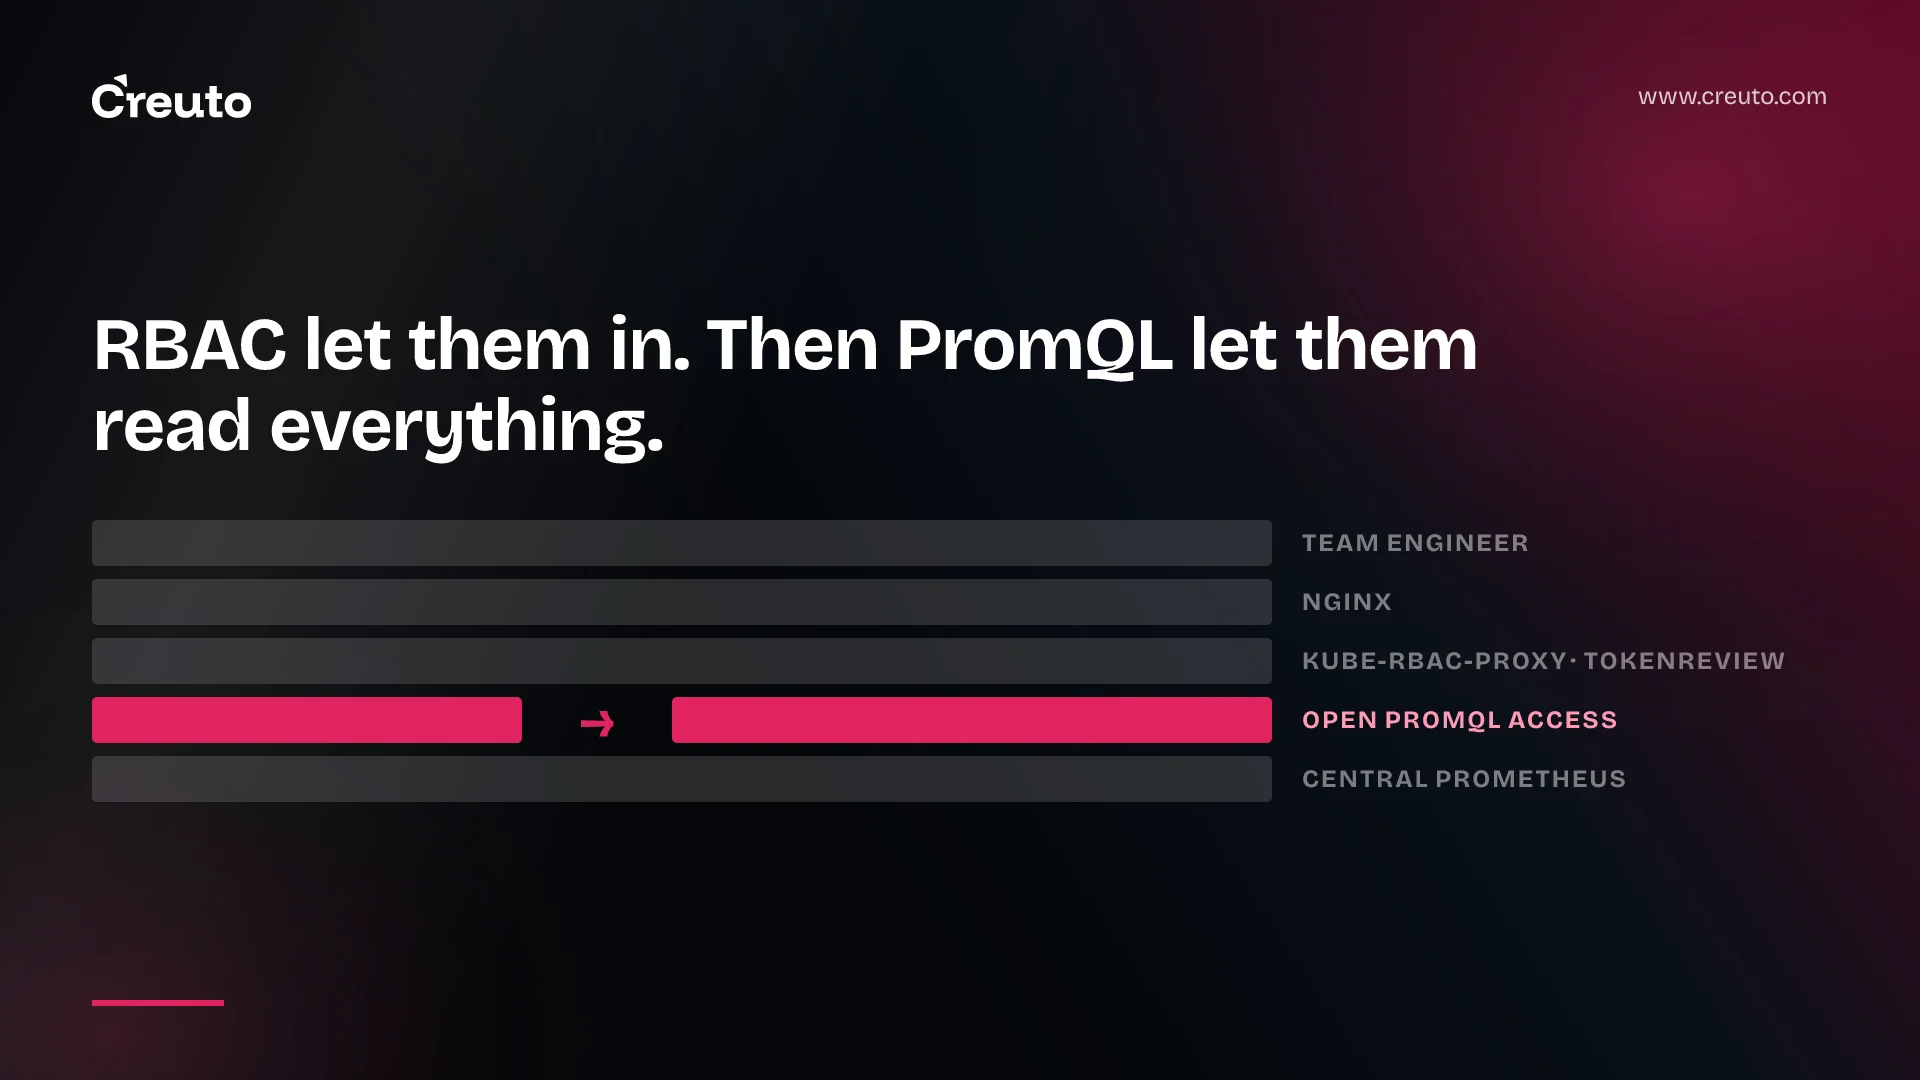
Multi-tenant Prometheus: let teams query their own metrics
Adobe engineers published a tenant-aware pattern for shared clusters: RBAC at the door, PromQL rewritten below the query language, and a custom resource so teams declare their own access. Here is where it still breaks.
Akash Mohapatra
Sep 29, 2026
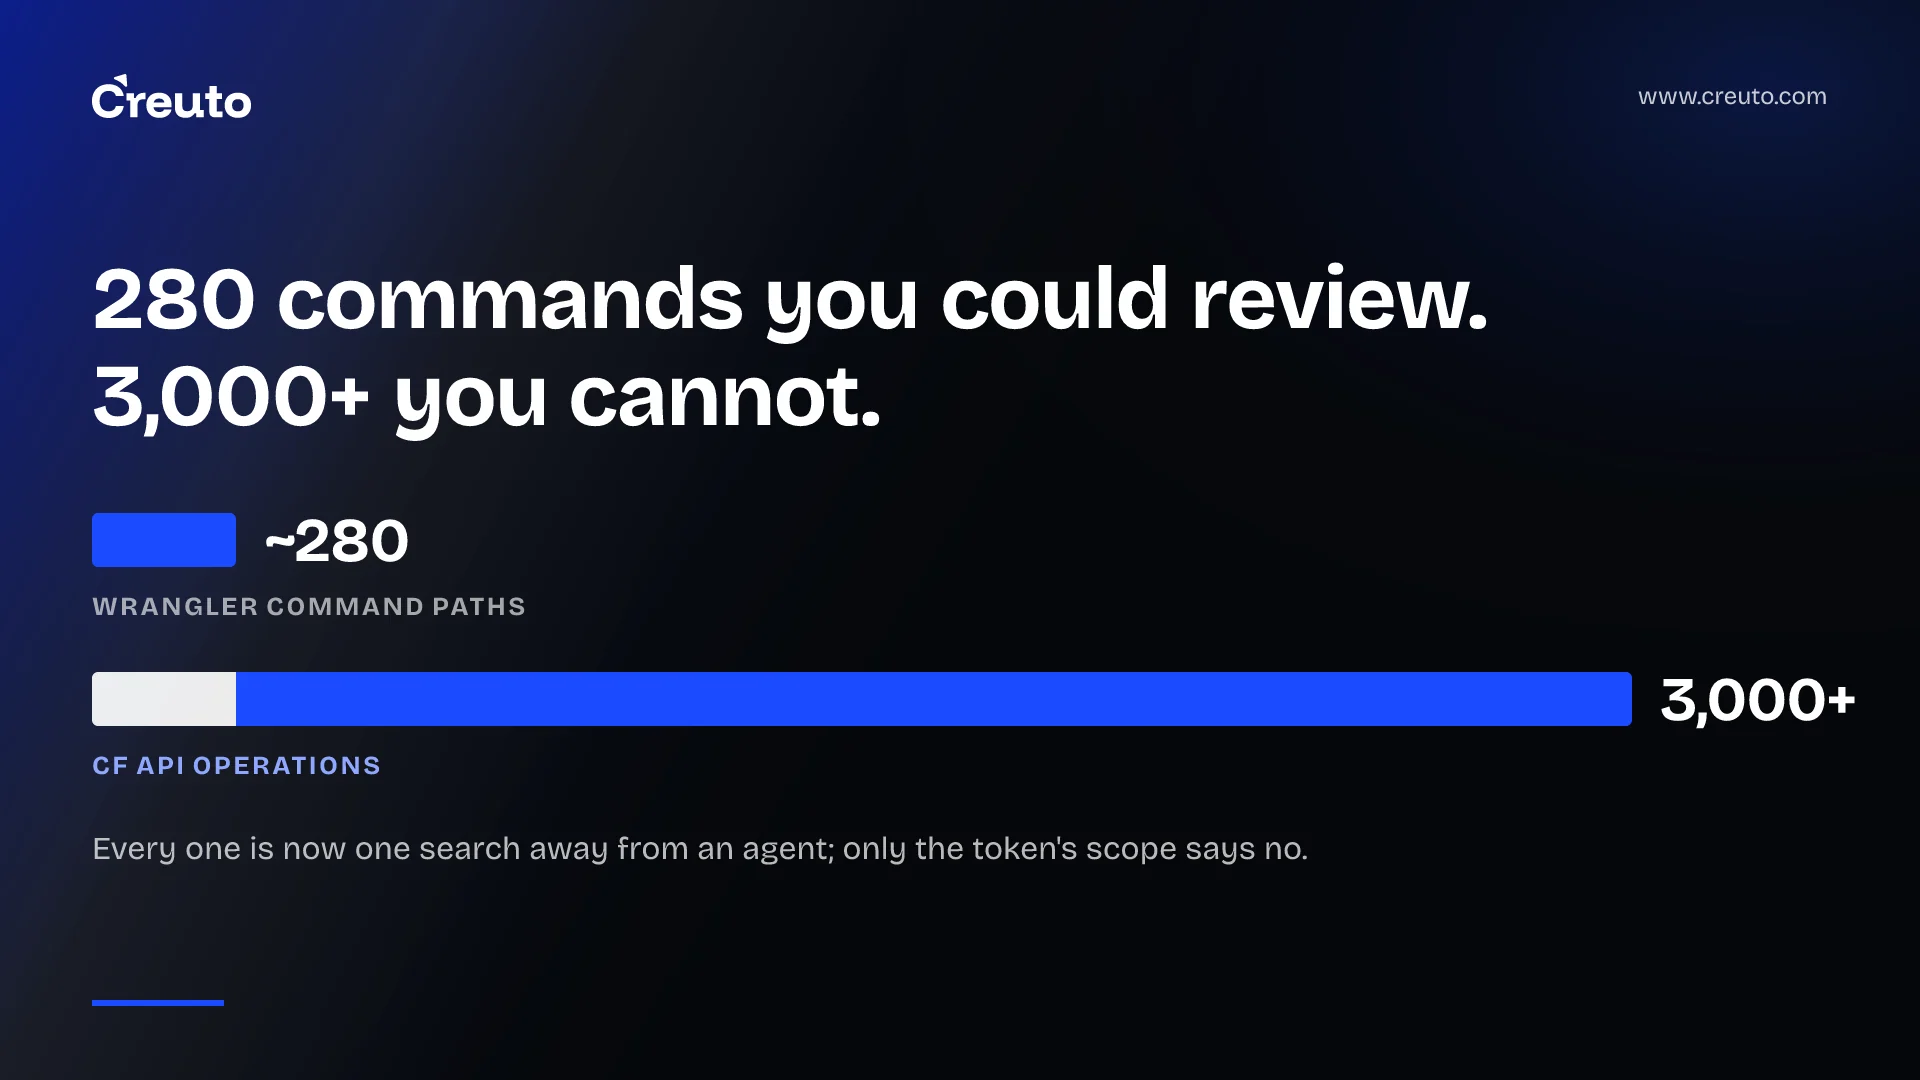
Cloudflare cf CLI: 3,000 API operations built for agents
Cloudflare's new cf CLI is generated from OpenAPI schemas and covers over 3,000 operations against Wrangler's ~280. The command surface is no longer a boundary, so the token's scope has to be.
Akash Mohapatra
Sep 29, 2026
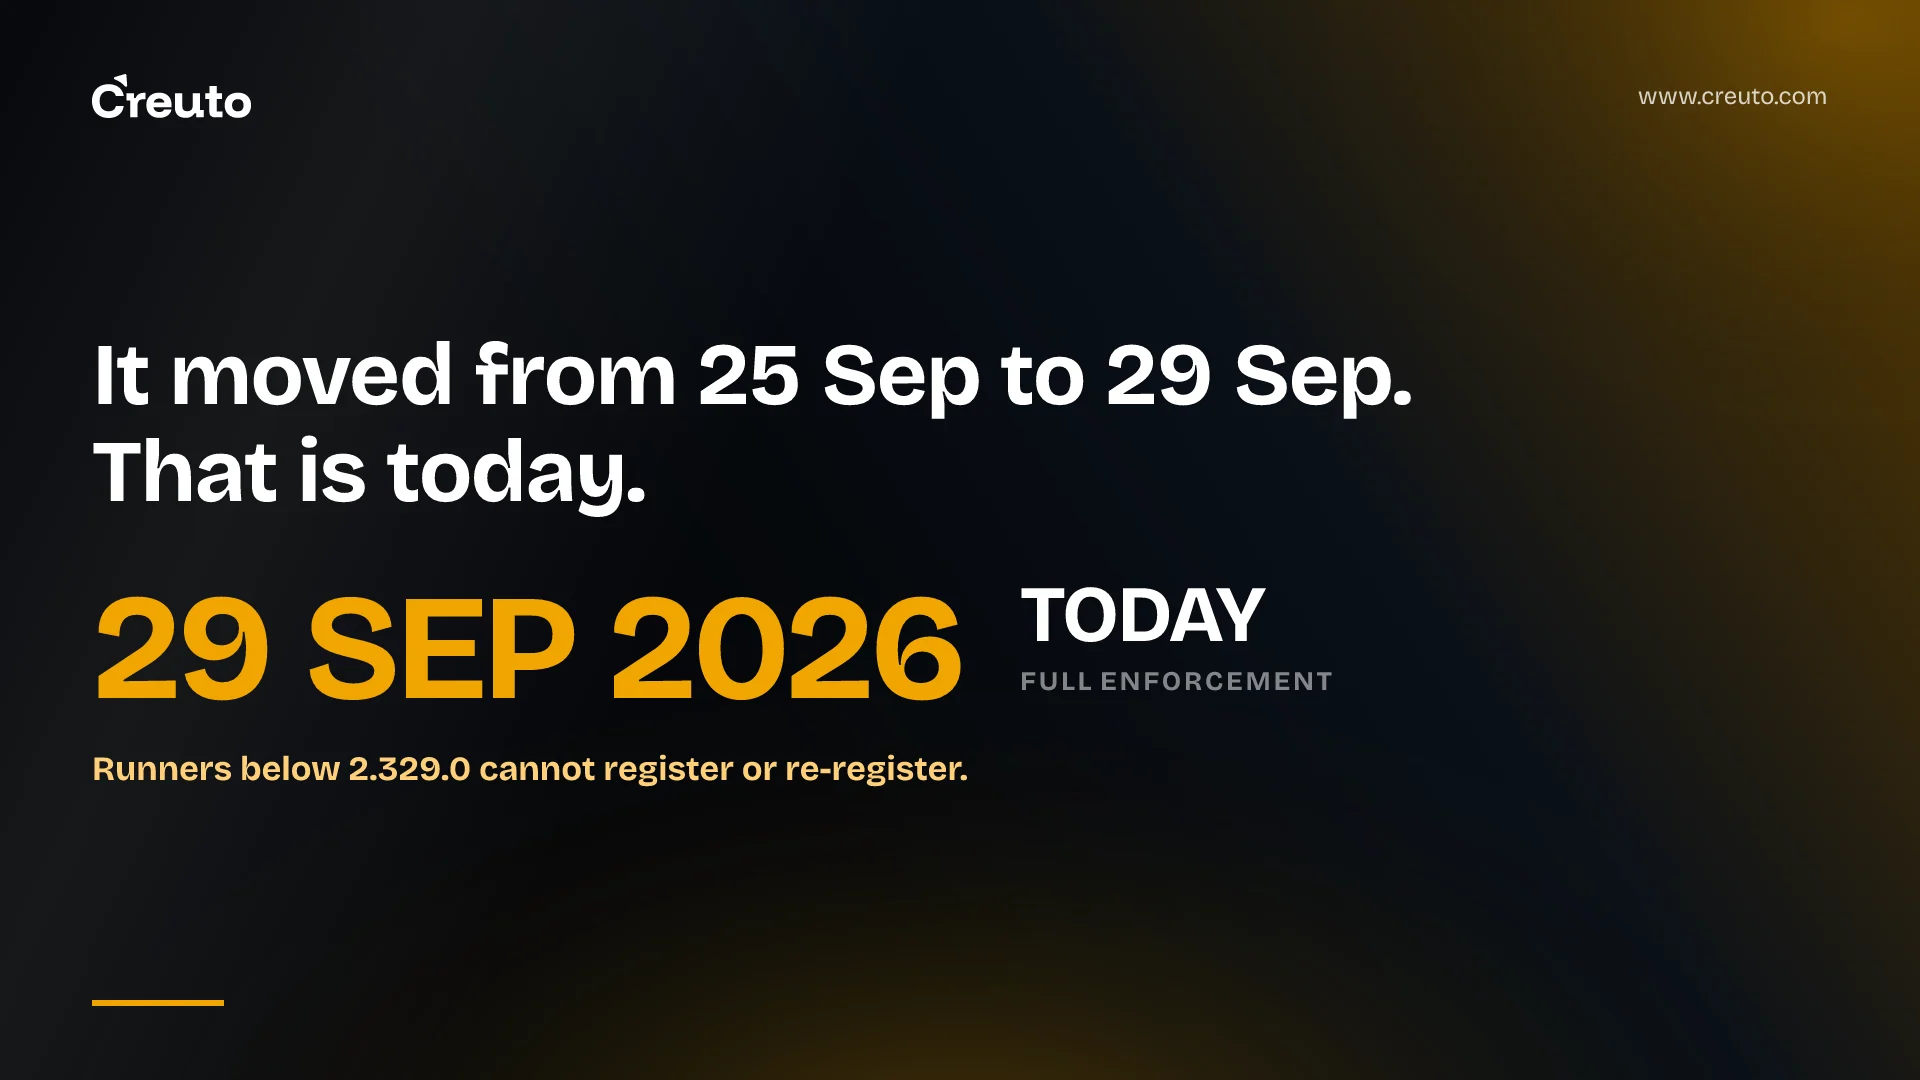
Self-hosted runner version 2.329.0 is enforced today
GitHub Enterprise Cloud enforces its minimum self-hosted runner version from 29 September 2026, four days later than planned. What breaks now, what breaks later, and how to audit a fleet with the new deprecations API.
Akash Mohapatra
Sep 29, 2026
GitHub proof of presence: re-auth before risky actions
GitHub's new proof of presence control re-verifies the person, not the session, before token creation, webhook edits and organization security changes. The public preview only reaches EMU enterprises on Entra ID.
Akash Mohapatra
Sep 26, 2026
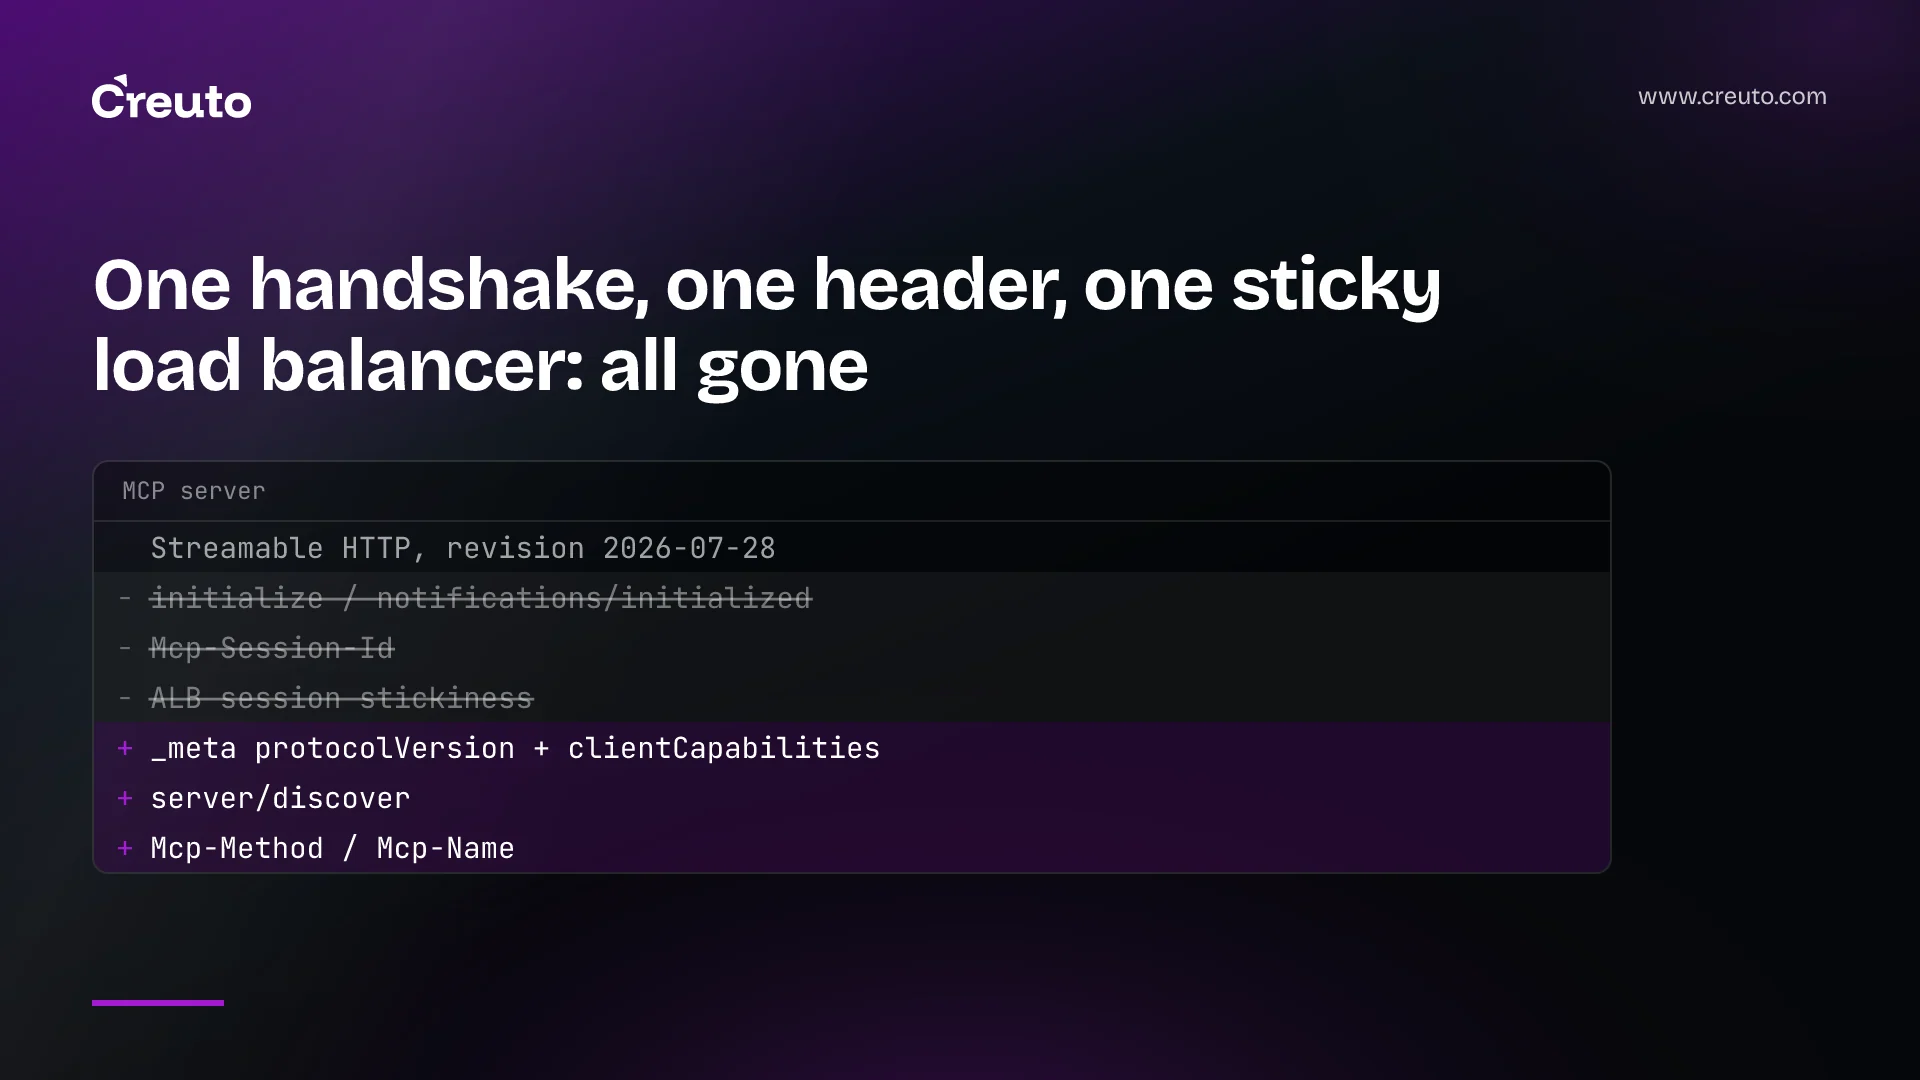
Stateless MCP: your server no longer needs sticky sessions
The 2026-07-28 MCP specification removed the initialize handshake and the Mcp-Session-Id header. Here is what that deletes from your AWS deployment, what older clients still need, and where application state belongs now.
Akash Mohapatra
Sep 26, 2026
One Vision. One Team. One Creuto.
Whatever your challenge, we bring the expertise to build, scale, and transform your digital presence with technology that works.